
USD 545.00
Currency
30-Day Money-Back Guarantee
Qty:

An ISMS audit isn't like auditing a quality system. You're not just checking whether procedures are followed – you're verifying that information assets are genuinely protected, that controls are working as designed, and that risks identified on paper are actually being managed in practice. That takes an auditor who understands both the 93 controls and how to gather evidence in an information security context.
This online Auditor training builds that capability. You'll learn how to interpret ISO/IEC 27001:2022 requirements from an auditor's perspective, evaluate controls across all four categories (Organizational, People, Physical, Technological), assess risk treatment plans, and document findings that drive real security improvements. Through a structured curriculum combining theoretical knowledge with practical application, you'll develop the competence to audit information security management systems against ISO/IEC 27001:2022.
The course is delivered entirely online and is self-paced, allowing you to progress through the material according to your own schedule. Upon successful completion, you will receive a certificate documenting your training as an ISO/IEC 27001 Auditor.
30-Day Money-Back Guarantee
If the course is not right for you, request a full refund within 30 days, provided you have not completed it.
An effective internal auditor does more than check compliance boxes. They help their organization identify improvement opportunities and strengthen information security. A competent ISO/IEC 27001 auditor must be able to:
This course develops these capabilities through structured lessons, practical examples, and audit resources you can apply immediately in your organization.
The training is organized into ten focused sessions that build your knowledge progressively. Sessions include:
Session 1: Overview of ISO/IEC 27001:2022 Information Security Management System
An introduction to ISO/IEC 27001 and the 2022 revision – its purpose, scope, and importance for information security. Understand what an ISMS is, why certification matters, and how the 2022 version differs from the 2013 version.
What you'll learn: The role of ISO/IEC 27001 in information security, the key changes in the 2022 revision, and what these changes mean for how you'll audit going forward.
Session 2: ISO/IEC 27001:2022 Requirements
A comprehensive clause-by-clause review of the ISO/IEC 27001:2022 standard. You will examine each requirement in depth, understanding what constitutes acceptable evidence of conformity in an information security context.
What you'll learn: Detailed understanding of ISO/IEC 27001 requirements and how to evaluate conformity during an internal audit.
Session 3: ISO/IEC 27001:2022 ISMS Controls
A detailed examination of all 93 controls organized into 4 categories: Organizational, People, Physical, and Technological. Learn about the 11 new controls introduced in the 2022 revision, including threat intelligence, cloud security, and secure coding.
What you'll learn: How to audit each control category and verify that controls are effectively implemented.
Session 4: Documented Information
A focused examination of documented information requirements for ISMS. Learn the distinction between documents and records and what documentation is typically required for ISO/IEC 27001 compliance.
What you'll learn: How to verify that ISMS documentation is properly maintained and controlled.
Session 5: Risk Management
Risk assessment and treatment are core to ISO/IEC 27001. This session covers the risk management process, including identifying information assets, assessing threats and vulnerabilities, determining risk levels, and evaluating risk treatment plans.
What you'll learn: How to audit risk management processes and verify that risk treatment is appropriate and effective.
Session 6: ISMS Internal Audit Process
This session introduces the complete internal audit cycle, from planning through follow-up. Learn audit methodologies, how to prepare for an ISMS audit, and how to conduct audit activities professionally.
What you'll learn: How to plan and conduct internal audits of information security management systems.
Session 7: ISMS Internal Audit Records
Audit proceedings and findings must be properly documented. This session covers audit preparation documentation, evidence gathering, audit reporting, and completion with follow-up activities including nonconformity reports.
What you'll learn: How to document audit activities and maintain records that demonstrate compliance.
Session 8: Terms and Definitions
Clear understanding of ISMS terminology is essential for effective auditing. This session defines key terms used in ISO/IEC 27001 and information security management.
What you'll learn: The vocabulary of information security auditing and how to apply terms correctly during audits.
Session 9: Steps for ISO/IEC 27001:2022 Installation and Certification
This session examines the complete implementation pathway, from initial gap analysis through certification audit. Understanding this process helps auditors provide valuable insights during internal audits.
What you'll learn: How organizations implement ISO/IEC 27001 and how internal audits support the certification process.
Session 10: Climate Action Changes – New Amendments (2024)
This session covers the latest amendments to ISO/IEC 27001 regarding climate action. Understand how climate change considerations are now integrated into the ISMS framework and what auditors need to verify.
What you'll learn: The 2024 climate action amendments and their implications for ISMS audits.
The course provides comprehensive resources that support learning and serve as valuable references:
This course is designed for people who will conduct assigned audit activities and contribute reliable evidence and findings to an internal audit program. It is particularly useful for:
The course is appropriate for those new to auditing as well as experienced professionals seeking to update their knowledge of ISO/IEC 27001:2022.
Note: If you need to lead audit teams, plan audit programs, or conduct third-party audits, the ISO 27001 Lead Auditor Training is a better choice.
The training program includes session exams and a comprehensive final examination. The assessments are in multiple-choice format and are designed to verify your understanding of the course material. To pass, you need a score of 60% or higher. If you do not pass on your first attempt, you may retake any exam at no additional charge.
Graduates receive an ISO/IEC 27001:2022 Auditor Certificate of Attainment bearing the Exemplar Global logo. It documents successful completion of the training and final examination and provides a pathway to apply for relevant Exemplar Global personnel certification.
The certificate also bears the IACET accreditation mark, and the course awards 1.6 IACET CEUs.
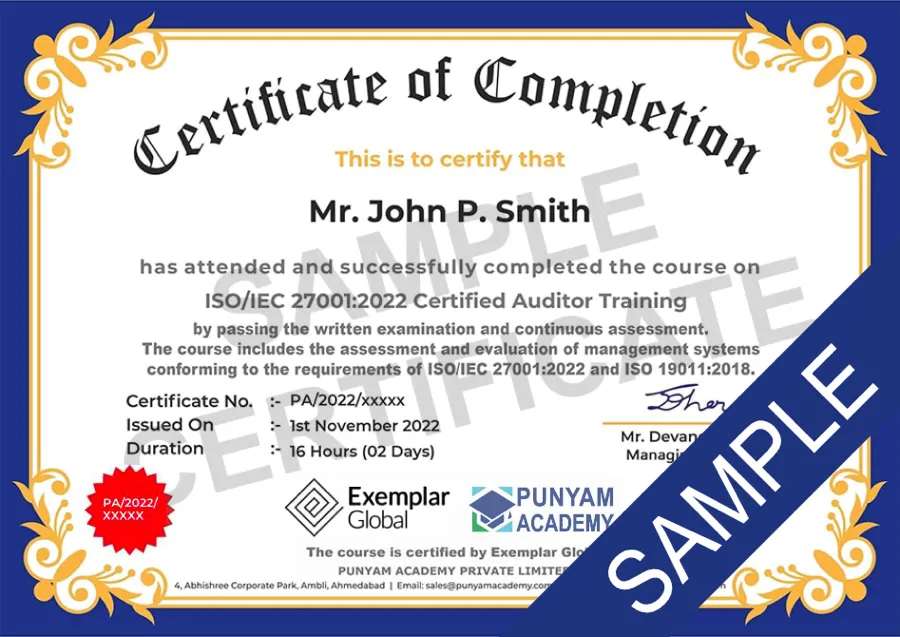
Certificates are issued in digital format upon passing the final examination. You may download, add to LinkedIn, and print your certificate directly from your course dashboard.
Training multiple internal auditors for your ISO/IEC 27001 information security management system? Our platform makes it simple to purchase multiple seats and manage enrollment across your organization.
Whether you’re training one internal auditor or building a team to cover your entire ISMS scope, the manager dashboard gives you oversight of every learner's progress.
Course access, materials, certificate plus manager dashboard for bulk enrollment.

Self-paced learning – fit the 16-hour program into your schedule without disrupting business.

Instructor access and technical support whenever you need assistance.

30-Day Money-Back Guarantee – enroll risk-free.

Instant access after enrollment with up to 3 months to complete.

Learn on any device – Windows, Mac, iOS, or Android.


Michael Brown
May 18, 2025
Clear and practical. Loved the handouts—150 pages is no joke, but they're well-organized and I still refer back to them when preparing reports. Icons like ...
Kevin Murphy
November 26, 2025
All those annex controls... it's quite a lot to memorize, and even to understand first. Luckily we can go back and repeat lessons as ...
Covers the 2022 Revision
Includes all 11 new controls and the restructured control categories – you're learning the current standard, not the 2013 version.

Practical Audit Techniques
Learn how to audit controls in practice – not just what the standard says, but what evidence to look for and what questions to ask.
400+ Audit Questions
Includes clause-wise and control-wise checklists you can adapt for audits of your own organization.
Professional Credential and Pathway
Earn a Certificate of Attainment bearing the Exemplar Global logo and gain a pathway to relevant Exemplar Global personnel certification.
You have up to three months. During that time, you can complete the training at your own pace and revisit earlier material.
Access ends when you successfully complete the final examination. Extensions are available for a fee if you need more time.
Auditor training prepares you to conduct assigned internal-audit activities as a team member.
Lead Auditor training covers additional competencies required to plan audits, lead audit teams, and manage the entire audit program.
Choose this Auditor course when you are beginning or contributing to an internal audit program.
The 2022 revision introduced 11 new controls and reorganized all 93 controls into 4 categories: Organizational, People, Physical, and Technological. Key additions include threat intelligence, information security for cloud services, ICT readiness for business continuity, and secure coding.
The course covers all these changes in detail, ensuring you can audit against the latest requirements.
Yes. The course includes a dedicated session (Session 10) on the Climate Action Changes amendments (2024) to ISO 27001, ensuring your knowledge is current with the latest standard requirements.
Yes. The 400+ question audit checklist provided with the course is designed to be a practical tool that you can customize and use for internal audits within your organization. It covers both clause-wise and control-wise questions.
There are no formal prerequisites. Familiarity with information-security operations is helpful, but the course teaches the ISO 27001 requirements and audit techniques you need.
Your purchase is protected by our 30-Day Money-Back Guarantee. If the course is not right for you, request a full refund within 30 days, provided you have not completed it.
Yes. Select the number of learners on this page and applicable volume discounts are applied automatically. A course manager can enroll the team and monitor progress from one dashboard.
When you purchase multiple seats, designate a course manager during checkout. The manager has up to 12 months to enroll the team. Once enrolled, each learner has up to three months to complete the course, and access ends upon successful completion of the final examination.
The charts below show our approval ratings based on post-course surveys from 2000+ learners. Enroll risk-free with our 30-Day Money-Back Guarantee.
(209)
USD 795.00
Lead complete ISO/IEC 27001 ISMS audits. Evaluate risk assessment and treatment, the Statement of Applicability, selected controls, evidence, and performance while directing audit teams. The certificate bears the Exemplar Global logo and supports application for relevant Exemplar Global personnel certification.
(1075)
USD 895.00
Perform assigned ISO 9001 audit activities as an effective internal audit-team member. Exemplar Global TPECS-certified online training with formal exam, unlimited retakes, Certificate of Attainment, and QM and AU Competency Units.
